
Research record from 12 November 2026. This article discusses published project research and implementation evidence, not independent certification.
Our federation research compared independent servers, portable identity and shared rooms, then documented why Commonveil chose a distinct encrypted protocol.
Three ideas worth combining
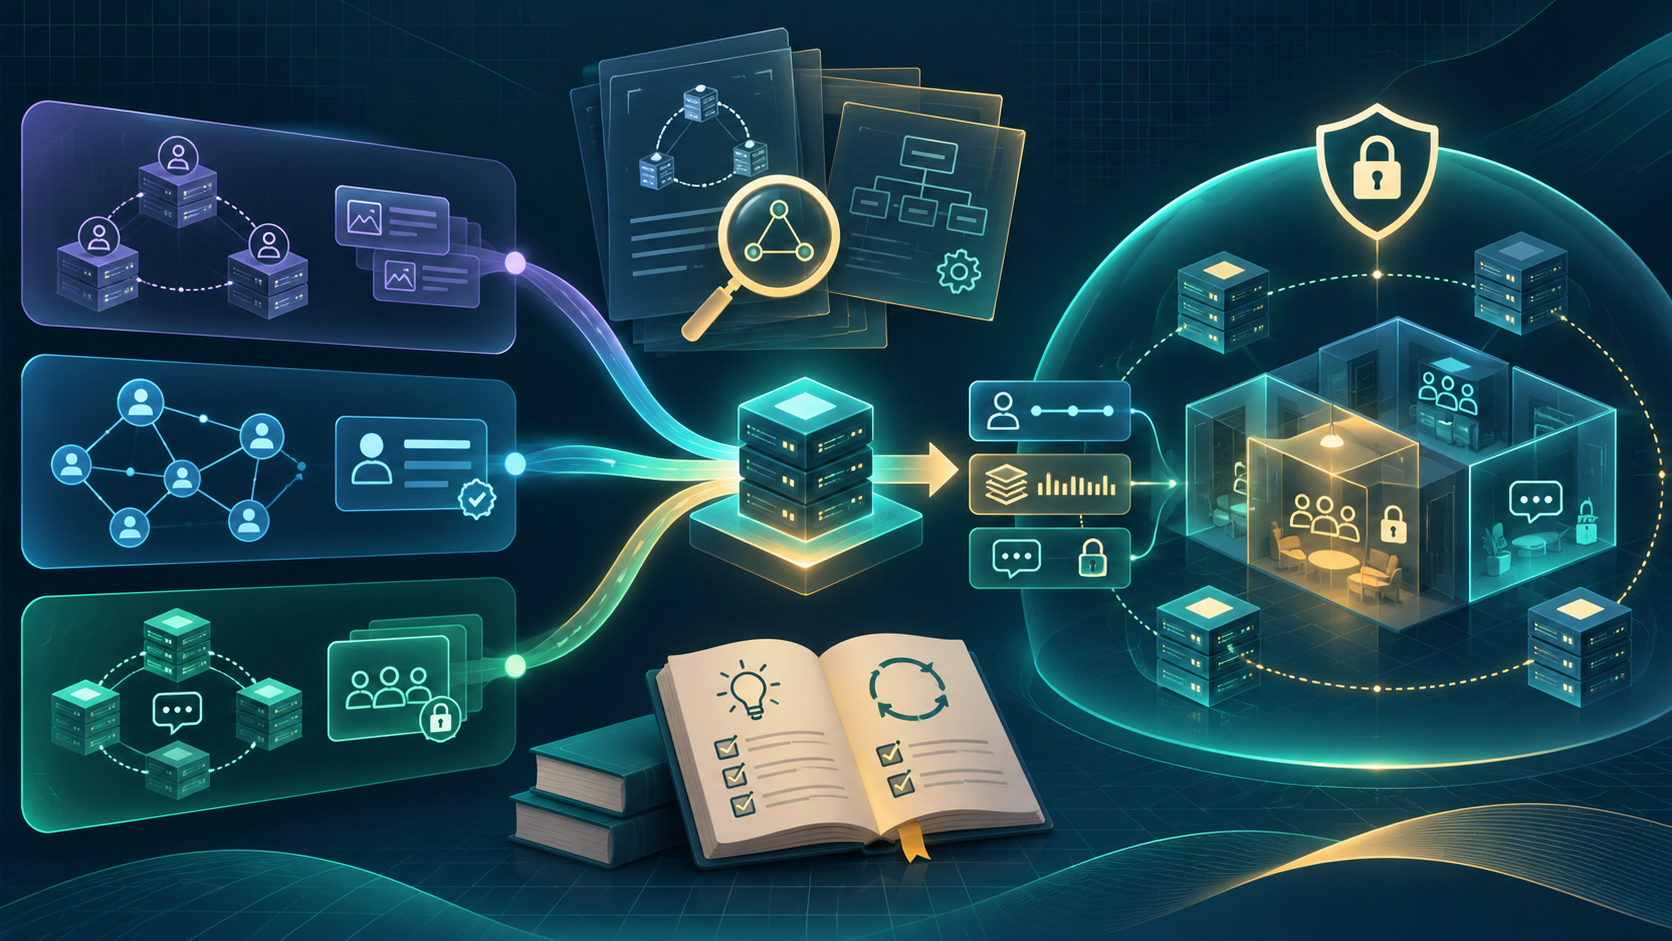
ActivityPub, AT Protocol and Matrix approach decentralised communication from different directions. Commonveil's federation document deliberately identifies the lessons drawn from each. ActivityPub provides a familiar model of independent servers exchanging signed requests and discoverable accounts. AT Protocol explores portable identity and repositories. Matrix shows how communities and rooms can span more than one server.
The aim was not to claim that one protocol had failed. Each has different architectural and compatibility constraints. Commonveil's particular requirement is that separately operated sites should relay private communication without acquiring the plaintext of messages they carry.
What the design adopted
Commonveil uses a home-site and host-site distinction. A member signs in to a home site, but may participate in a conversation hosted somewhere else. The home signs a request, the host checks that site and the member's permissions, and the actual message stays encrypted for participating devices. A shadow identity at the host carries only the details needed for authorisation, such as public keys and a reference to the home identity.
From ActivityPub-style infrastructure it borrows independently operated sites, signed server requests and discovery ideas such as WebFinger. From AT Protocol it takes inspiration for domain-based identity. From Matrix it takes the expectation of cross-site communities and rooms.
What was deliberately different
The documented Commonveil model does not simply replicate a room's full history across every participating site. A conversation has one host, and other sites relay access for their own members. This limits how widely encrypted records are duplicated, at the cost of depending on the host's availability. Other resilience mechanisms must address outages explicitly.
Nor is Commonveil's encrypted wire format automatically compatible with ActivityPub or AT Protocol. Their public social formats do not define the same private session and key rules. Bridges for public data may be possible later, but compatibility must be demonstrated with a real bridge rather than inferred from shared vocabulary.
Security and portability questions
Federation adds trust boundaries. Each site has a published identity key; other sites pin that key and reject unexpected changes until an operator approves them. Requests are signed with relevant parameters and a freshness check to reduce impersonation and replay. Client devices must still verify user keys; trusting the relay's account database alone is insufficient.
A portable account needs more than a new handle. Devices, contacts, proof of ownership, encrypted history and moderator decisions can all affect a move. The social protocol research later proposed signed repositories and actor keys to address part of that problem, but deployment and independent interoperability testing remain separate tasks.
Implementation status and findings
The Commonveil repository documents federation endpoints and tests in which two self-hosted sites communicate. It also records a hosted-site bridge and later sealed-relay work. Those source records are evidence of implemented engineering paths, not proof that every third-party platform can talk to Commonveil today.
The main finding is that decentralisation should reduce dependence without making security guarantees untestable. A protocol may adopt useful concepts from other networks and still need its own honest compatibility matrix, documentation and external testers.
Primary sources and further reading
Explore other Comutability research · Read about the organisation