
Research record from 12 November 2026. This article discusses published project research and implementation evidence, not independent certification.
Secure Net's interoperability research explores how independent sites can exchange signed, encrypted messages without trusting each other's databases.
The fundamental question
How can someone using one independent server communicate with someone on another when neither server operator should have to trust the other's database? The Secure Net interoperability guide starts with a distinction between transport and identity. Servers deliver information, but the user's keys and signed device statements are meant to establish who created it.
That matters because conventional federation may put too much authority in the server serving an account. If a server can silently replace keys and issue messages on the user's behalf, moving between operators does not necessarily make the network self-sovereign.
Three rules emerging from the design
First, account and device keys carry cryptographic identity. Device certificates and chains of key statements are checked by clients. Key changes after initial contact should trigger an observable warning when they do not follow the expected chain. A user can compare safety numbers when the first contact is important.
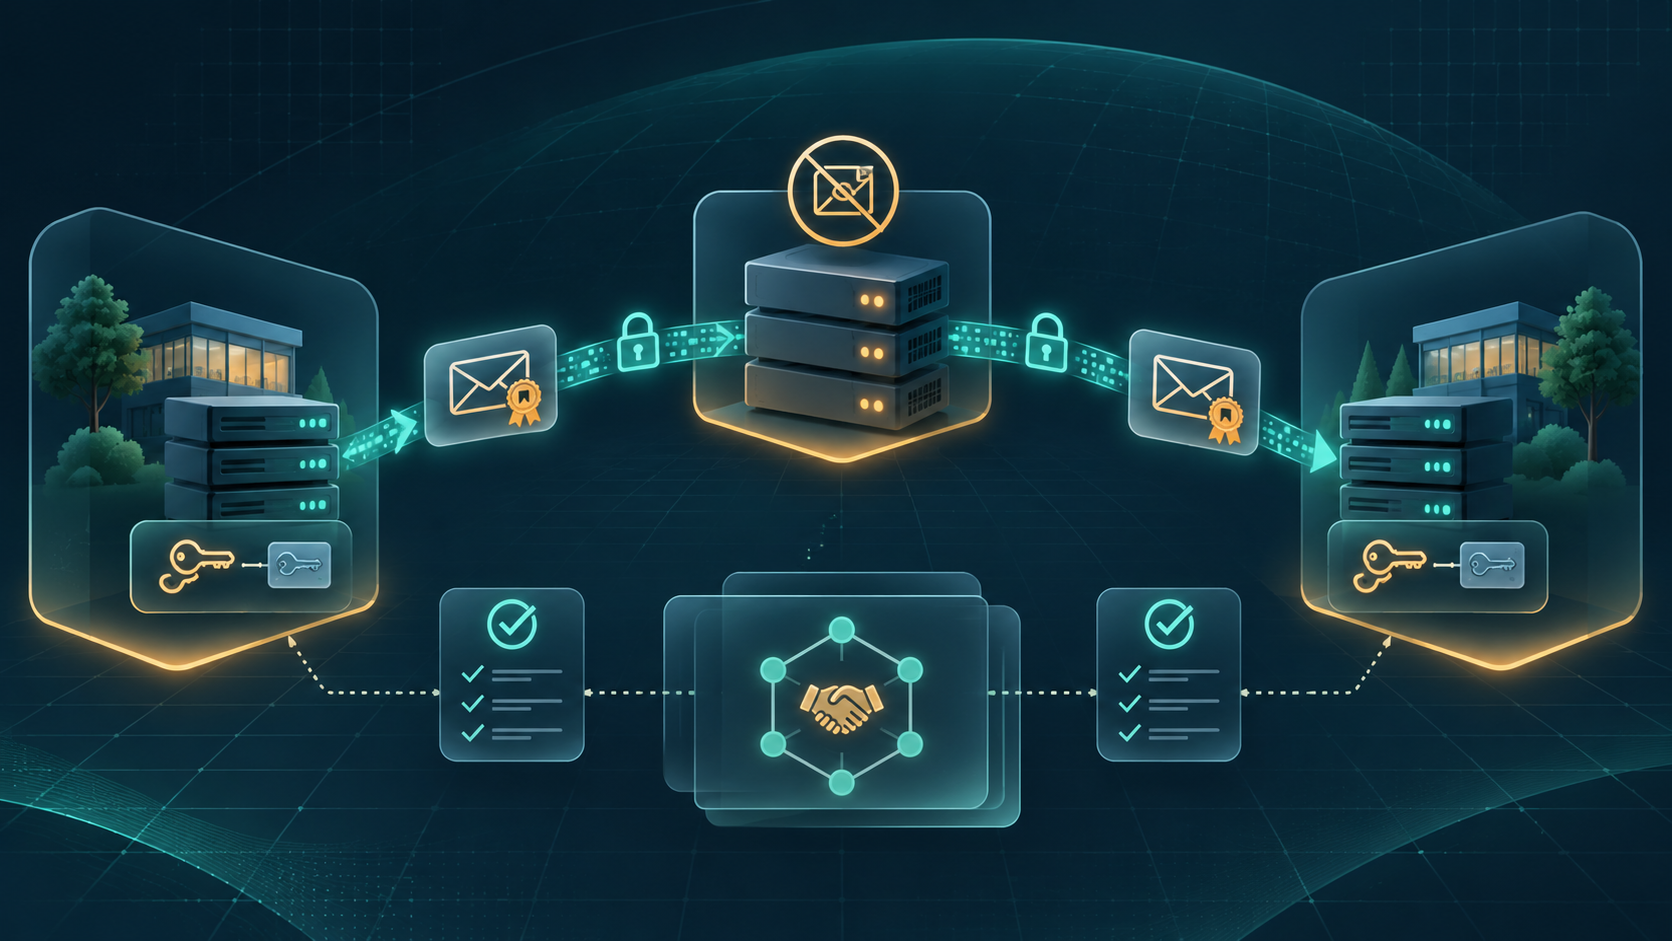
Second, sites have their own keys and sign requests over the destination, method, path, time, one-off nonce and body digest. The protocol can reject stale or repeated requests. Third, both sides use agreed byte-exact formats and feature declarations. Neither should need to read the other site's storage to know how to validate a record.
A two-site message journey
Imagine a person on Site A contacting a person on Site B. The first client's software requests the recipient's identity and device information through the federation route, then checks the returned key chain. It encrypts the content for authorised devices before handing ciphertext to its home site. Site A signs the delivery to Site B. Site B validates the site request, stores ciphertext and gives it to the recipient's device.
The destination client verifies the sender's identity and opens the message. Both sites remain operational intermediaries, so they can delay or refuse delivery. Neither should be able to decrypt content solely because it operates a database.
What information is still exposed
The interoperability guide explicitly records that sites can learn who communicates with whom, when messages travel and approximately how much traffic is exchanged. Network observers can identify which sites exchange data. Federation is not anonymity, and a safety-number comparison does not hide a sender's IP address from every possible observer.
This is why later research considered sealed sending, encrypted relays and metadata limits, rather than treating encrypted bodies as the end of the privacy problem.
Implementation and open work
The guide references the Secure Net crypto, core and wire components, plus Commonveil's self-hosted federation as an implementation route. Compatible independent implementations still need to pass conformance tests and security review. The documented model is a technical target, not a guarantee that any arbitrary third-party server is already compatible.
The finding worth retaining is that independence comes from verifiable shared rules, not a requirement to trust the same provider. Those rules must be simple enough to implement and strict enough to reject malformed or misleading traffic.
Primary sources and further reading
Explore other Comutability research · Read about the organisation